



PW Consulting: Incident Response Market Hits $35.2B in 2025, Poised for 18.52% CAGR to 2032

Navigating the New Reality: Strategic Imperatives in the 2026 Incident Response Landscape
The cybersecurity landscape has undergone a fundamental transformation. No longer viewed merely as a technical contingency, incident response (IR) has emerged as a core business continuity function and a critical component of enterprise risk management. As organizations grapple with increasingly sophisticated attack vectors, regulatory pressures, and the operational complexities of hybrid work environments, the ability to detect, contain, and recover from security incidents with speed and precision has become a defining competitive advantage.
This article serves as an introduction to the latest market research publication from PW Consulting, designed to equip executive leaders, security architects, and investment strategists with the comprehensive intelligence needed to navigate the Incident Response market through 2032. The following analysis highlights the market trajectory, structural dynamics, and strategic considerations that will shape decision-making in 2026 and beyond. Readers seeking the full granular segmentation, regional revenue breakdowns, competitive benchmarking matrices, and actionable investment roadmaps are invited to access the complete report through our dedicated source page.
Worldwide Information Security Market
Market Trajectory: A Sector Defined by Accelerated Expansion
The Incident Response market has demonstrated remarkable resilience and growth over the past half-decade, transitioning from a reactive cost center to a proactive strategic investment. Historical data from 2020 through 2025 illustrates a consistent upward trajectory, with the overall market expanding from approximately 22.41 billion USD in 2020 to 35.2 billion USD by 2025. This growth reflects a broader industry recognition that traditional perimeter defenses are insufficient against modern threat actors, driving enterprises to allocate significant capital toward integrated response capabilities.
Projecting forward into the forecast period spanning 2026 to 2032, the market is poised for sustained momentum. The sector is expected to reach 40.7 billion USD in 2026, with growth accelerating steadily to approximately 50.71 billion USD by 2027, 59.83 billion USD by 2028, and continuing through to an estimated 116.17 billion USD by 2032. This expansion is underpinned by a compound annual growth rate (CAGR) of 18.52 percent, signaling one of the most robust growth profiles within the broader cybersecurity ecosystem.
Such momentum is not merely a function of increased spend; it reflects a structural shift in how organizations value resilience. The compounding effect of this growth trajectory suggests that incident response will increasingly intersect with board-level discussions around digital transformation, insurance underwriting, and regulatory compliance. Decision-makers operating without a clear view of this trajectory risk misallocating resources or falling behind competitors who are already embedding IR capabilities into their enterprise architecture.
Structural Dynamics: What Is Driving Demand in 2026
Regulatory and Compliance Imperatives
The regulatory environment has become a primary catalyst for incident response adoption. In May 2026, the Cybersecurity and Infrastructure Security Agency (CISA) rescheduled virtual town hall meetings regarding the proposed rule for the Cyber Incident Reporting for Critical Infrastructure Act of 2022, with proceedings set to begin on June 15, 2026. The proposed rule mandates that critical infrastructure organizations report cyber incidents to CISA within 72 hours and ransom payments within 24 hours. These tightening timelines create an acute operational requirement for organizations to have established response protocols, forensic capabilities, and communication frameworks ready before an incident occurs, rather than improvising under pressure.
For enterprises across critical sectors, compliance is no longer a checkbox exercise. It demands documented playbooks, trained response teams, and integrated tooling that can capture evidence and execute containment in real time. Organizations that treat IR as a compliance function alone will find themselves exposed; those that treat it as a strategic capability will gain both regulatory alignment and operational resilience.
The Multi-Vector Threat Reality
Threat actor methodology has evolved significantly. According to the 2026 Unit 42 Global Incident Response Report from Palo Alto Networks, which analyzed over 750 major cyber incidents investigated in 2025, 87 percent of intrusions involved activity across multiple attack surfaces. This finding underscores a critical reality: organizations can no longer afford siloed security operations where endpoint, network, cloud, and identity domains operate in isolation.
The implication for the incident response market is profound. Response capabilities must be orchestrated across the entire attack surface, integrating telemetry, automation, and human expertise into a unified workflow. This multi-vector reality is pushing enterprises toward managed detection and response arrangements, platform-based analytics, and retainer-based professional services that can scale during active incidents. The market is responding accordingly, with growth distributed across containment, mitigation, remediation, recovery, digital forensics, and analytics functions.
The Preparedness Gap
Despite increased investment, a troubling disconnect persists between planning and operational readiness. Sygnia's 2026 CISO Survey, titled The State of Incident Response Readiness, highlighted that many organizations maintain documented incident response plans that do not translate into effective execution during real-world events. This gap between theoretical preparedness and practical capability represents both a risk and an opportunity. It creates demand for services that bridge the divide: tabletop exercises, retainer engagements, rapid deployment forensics teams, and technology that reduces the cognitive load on responders during high-pressure situations.
Market Scope and Segmentation: A High-Level View
The Incident Response market encompasses a diverse set of services and solutions, reflecting the multifaceted nature of modern threat response. At a high level, the market can be understood through several structural dimensions that collectively define how organizations procure and consume IR capabilities.
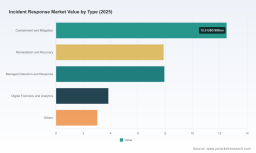
- Response and Recovery Functions: The market is anchored by containment and mitigation capabilities, complemented by remediation and recovery services that restore operational integrity after an incident. Managed detection and response arrangements have gained significant traction, offering organizations continuous monitoring and rapid intervention without the need to build fully in-house capabilities. Digital forensics and analytics provide the evidentiary and investigative backbone necessary for both internal decision-making and external reporting obligations.
- Application Across Sectors: Incident response demand is broad-based, spanning highly regulated industries such as financial services and government and defense organizations, as well as technology and telecommunications providers, energy and utilities operators, and a range of other sectors. Each vertical brings distinct compliance requirements, threat profiles, and operational constraints that shape how response capabilities are deployed.
- Geographic Distribution: Demand is distributed across major global regions, with North America representing a substantial share, followed by Europe and Asia Pacific. Latin America and the Middle East and Africa represent emerging growth zones where regulatory maturation and threat landscape evolution are driving incremental investment.
The complete report provides detailed revenue distributions across each segmentation dimension, including regional breakdowns, service-type allocations, and vertical-specific demand patterns. These granular insights are essential for organizations seeking to benchmark their own positioning, identify underserved niches, or evaluate partnership opportunities within specific market pockets.
Competitive Landscape: Leaders, Specialists, and Emerging Models
The Incident Response market is characterized by a mix of platform-centric technology vendors, professional services firms, and specialized response boutiques. Market concentration data indicates that the top three competitors command approximately 48 percent of total market revenue, while the top five collectively represent around 68 percent. This concentration reflects the dominance of large, integrated players who offer end-to-end capabilities spanning detection, response, forensics, and managed services. However, significant opportunity remains for specialized firms that deliver deep expertise, retainer-based engagements, and sector-specific knowledge.
Platform Leaders and Integrated Ecosystems
Several prominent organizations define the current competitive landscape. CrowdStrike, headquartered in San Francisco, offers the Falcon platform with managed detection and response capabilities, integrating advanced incident response functions within a unified endpoint and cloud security ecosystem. SentinelOne, based in Mountain View, provides the Singularity Platform and Vigilance Respond services, leveraging AI-powered endpoint detection and response to support incident response workflows. Palo Alto Networks, located in Santa Clara, delivers Unit 42 global incident response services alongside Cortex XDR and Prisma Access solutions, combining threat intelligence with operational response capabilities.
IBM, headquartered in Armonk, provides IBM Security QRadar alongside professional incident response services, offering enterprises a combination of SIEM-driven analytics and expert intervention. Cisco Systems, based in San Jose, delivers incident response capabilities through the Cisco SecureX platform, emphasizing integration across network, endpoint, and cloud security domains. Rapid7, located in Boston, offers InsightIDR and automated incident response automation tools, focusing on reducing mean time to respond through orchestrated workflows. Sophos, also headquartered in Boston, provides MDR and incident response through its Sophos MDR and EDR solutions, targeting mid-market and enterprise customers with managed security offerings.
Specialized Services and Retainer-Based Models
Alongside platform providers, a cohort of professional services and specialized response firms plays a critical role in the ecosystem. NCC Group, based in London, offers professional incident response retainer and investigation services, providing clients with pre-arranged access to expert teams during active incidents. Kroll, headquartered in New York, delivers comprehensive digital forensics and global incident response recovery services, serving organizations that require deep investigative capabilities and cross-border response support. Beazley, also based in London, delivers cyber incident response services as part of broader cyber and data resilience offerings, often intersecting with insurance and risk transfer frameworks.
Optiv Security, located in Reston, offers managed security services and incident response retainer programs, helping organizations bridge the gap between technology deployment and operational execution. Check Point Software Technologies, headquartered in Tel Aviv, provides incident response through its solution portfolio and professional services, supporting organizations that seek integrated threat prevention alongside response capabilities.
Recent Market Movements and Strategic Shifts
The competitive landscape continues to evolve through partnerships, publications, and market recognition. In March 2026, LevelBlue announced an expanded global strategic partnership with SentinelOne to deliver AI-powered managed security operations and incident response, signaling a trend toward combining managed service delivery with advanced platform capabilities. In April 2026, Palo Alto Networks published the 2026 Unit 42 Global Incident Response Report, providing detailed insights from over 750 major cyber incidents investigated in 2025 and reinforcing the importance of cross-surface visibility.
Sygnia made notable strides in April 2026, releasing the 2026 CISO Survey that highlighted gaps between incident response planning and operational readiness, while also being named a Representative Vendor in the 2026 Gartner Market Guide for Cybersecurity Incident Response Retainer Services. These developments underscore a market that is maturing in its understanding of what effective response requires: not just technology, but validated processes, trained personnel, and pre-established relationships that can be activated at a moment's notice.
Strategic Considerations for 2026 Decision-Makers
As organizations evaluate their incident response strategy for 2026 and beyond, several strategic considerations merit focused attention. These considerations extend beyond technology procurement to encompass organizational design, vendor selection, regulatory alignment, and investment prioritization.
Build, Buy, or Partner: Defining the Operating Model
One of the most consequential decisions facing enterprises is the structure of their incident response capability. Some organizations pursue a fully in-house model, building internal teams, acquiring platform tools, and developing internal playbooks. Others rely heavily on managed detection and response providers or professional services retainers. The optimal approach is rarely binary. Most mature organizations adopt a hybrid model: maintaining internal oversight, governance, and critical decision-making authority while leveraging external partners for surge capacity, specialized forensics, and 24/7 monitoring coverage.
Determining the right mix requires a clear understanding of internal maturity, risk tolerance, budgetary constraints, and the specific threat profile of the organization. The complete report provides frameworks for evaluating these trade-offs, including comparative analyses of service models, cost structures, and performance outcomes across different operating approaches.
Incident Response Market
Integrating Response with Broader Security Architecture
Incident response cannot function effectively in isolation. It must be integrated with preventive controls, threat intelligence, identity management, and data protection programs. Organizations that treat response as a standalone function often encounter friction during incidents: telemetry is siloed, containment actions are delayed by cross-team dependencies, and recovery processes conflict with business continuity requirements.
A more effective approach embeds response capabilities within a layered security architecture, ensuring that detection signals flow seamlessly into response workflows, that containment actions are coordinated across endpoint, network, and cloud domains, and that recovery processes are aligned with organizational resilience objectives. This integration also supports compliance objectives, particularly as reporting timelines tighten under emerging regulatory frameworks.
The Role of Automation and AI in Response Operations
Automation and artificial intelligence are increasingly central to incident response effectiveness. AI-powered endpoint detection, automated triage, and orchestrated response playbooks can significantly reduce the time between detection and containment, which is critical given the speed at which modern threats propagate across multiple attack surfaces. However, technology alone is insufficient. Automation must be paired with clear escalation paths, human judgment for complex decision-making, and regular testing to ensure that automated actions produce the intended outcomes.
The market is seeing growing demand for solutions that combine AI-driven detection with human-led investigation and response, particularly in scenarios that require contextual understanding, legal considerations, or coordination with law enforcement and regulators. Organizations evaluating technology investments should prioritize platforms that support this human-machine collaboration rather than treating automation as a wholesale replacement for expert response.
Preparedness as a Continuous Discipline
The gap between planning and operational readiness identified in recent industry surveys points to a broader truth: incident response is not a one-time project but a continuous discipline. Organizations that treat response readiness as a static deliverable, such as a documented plan filed away after an initial assessment, will find themselves ill-prepared when an actual incident occurs. Effective readiness requires regular testing through tabletop exercises and simulated incidents, ongoing training for response teams, periodic review of playbooks against evolving threat intelligence, and established relationships with external responders that can be activated under pressure.
For organizations operating in regulated sectors, readiness also encompasses documentation, evidence preservation, and reporting workflows that align with legal and regulatory obligations. Treating these elements as integral components of response capability, rather than afterthoughts, will differentiate resilient organizations from those that struggle during incidents.
Why This Research Matters: Turning Intelligence into Action
Market research in the incident response space must go beyond high-level growth figures and surface-level trend summaries. Decision-makers need actionable intelligence that connects market dynamics to concrete strategic choices: where to invest, how to structure partnerships, which capabilities to prioritize, and how to position an organization for both risk mitigation and competitive advantage.
The full PW Consulting Incident Response Market report delivers this depth. It provides comprehensive segmentation analysis across regions, service types, and application verticals, enabling readers to benchmark their own market positioning and identify growth opportunities. It offers detailed competitive profiling of key market participants, including technology capabilities, service offerings, recent strategic moves, and market share dynamics. It examines regulatory developments, threat landscape evolution, and operational challenges that are shaping demand, with a particular focus on implications for 2026 and the forecast period through 2032.
For enterprise leaders, the report serves as a decision-support tool for aligning security investments with business objectives. For investors and market analysts, it provides a data-rich view of market structure, growth drivers, and competitive positioning. For vendors and service providers, it offers insights into demand patterns, customer priorities, and emerging opportunities across different segments of the incident response ecosystem.
Accessing the Complete Intelligence
This article has provided a strategic overview of the Incident Response market, highlighting growth trajectory, structural dynamics, competitive landscape, and key considerations for 2026 decision-making. However, the full scope of intelligence available in the complete PW Consulting report extends well beyond this summary. Detailed revenue breakdowns by region, type, and application; competitive benchmarking across all profiled companies; granular analysis of regulatory impacts and threat trends; and actionable recommendations for investment and operational planning are all contained within the full publication.
To access the complete dataset, competitive matrices, segmentation deep-dives, and strategic frameworks, visit the dedicated source page for the Incident Response Market research. The full report is designed to support executive briefings, investment committee discussions, vendor evaluation processes, and long-term strategic planning, providing the comprehensive intelligence needed to navigate a market defined by rapid growth, evolving threats, and increasing regulatory complexity.
The incident response landscape will continue to evolve at a pace that demands informed, proactive decision-making. Organizations that invest in understanding the market's structure, dynamics, and trajectory will be best positioned to build resilience, meet compliance obligations, and turn incident response from a reactive necessity into a strategic capability. The complete PW Consulting report provides the foundation for that understanding.
For detailed analysis of this topic, please visit the official page: Incident Response Market
Lacy Lee
Senior Marketing Manager
sales@pmarketresearch.com
00852-95632430
PW Consulting: www.pmarketresearch.com
Tags



PW Consulting
The Best-reviewed Subdivided Market Risk Analysis Firm in the US and East Asia.


