



PW Consulting Predicts Anti‑Tamper Software Market to Expand at a 15.0% CAGR During 2026–2032, Ushering in a New Wave of Security Innovation

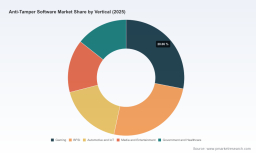
Anti-Tamper Software Market 2026: Strategic Imperatives from PW Consulting’s New Industry Brief
PW Consulting’s latest market brief on Anti-Tamper Software offers a concise, actionable intelligence set designed for executives who must make procurement, engineering and program-protection decisions in 2026. Built on a base year of 2025 and a rigorous forecast through 2032, the study synthesizes historical adoption patterns, regulatory pressures and vendor behaviors into a decision framework that helps CIOs, CISO teams, procurement leads and product owners move from risk recognition to operational deployment.
Anti Tamper Software Market
Market Snapshot: Momentum, Magnitude, and the Macro Trajectory
The anti-tamper software market has transitioned from niche defense and gaming origins into a mainstream element of application and device lifecycle protection. Our base-year analysis (2025) values the global market at approximately USD 757.5 million and shows a doubling of market value since 2020, when the market was roughly USD 380 million. With a compound annual growth rate (CAGR) of 15.0% over our forecast window (2026–2032), PW Consulting projects the market to surpass the USD 2.0 billion mark by 2032—making anti-tamper no longer optional for organizations that rely on software integrity as a competitive or regulatory differentiator.
Anti Tamper Software Market
This growth is not uniform by use case or geography (the brief contains the granular breakouts), but the macro drivers are clear: increasing regulatory expectations, proliferation of connected endpoints, higher-value digital assets, and the commoditization of tamper tooling.
Anti Tamper Software Market
Why This Brief Matters for 2026 Decisions
- Procurement clarity: Buyers struggle with vendor claims—this brief supplies an operational scoring model that prioritizes platform compatibility, runtime assurances, and verifiable tamper detection.
- Architecture trade-offs: Cloud-native protections vs. on-prem and hardware-assisted approaches require different engineering investments; we show the breakpoints for when each approach becomes economically and operationally optimal.
- Regulatory alignment: The brief maps anti-tamper capabilities to compliance regimes (e.g., SOX, HIPAA, FISMA) and defense policies (including U.S. DoD anti‑tamper guidance), so security and compliance teams can demonstrate mapped controls in audits and program-protection plans.
- Operational cost forecasting: We quantify labor and DevSecOps skill requirements for modern anti‑tamper integrations and model total cost of ownership under multiple adoption scenarios.
Dynamics Shaping 2026 Strategy
- Regulations and program-protection policy: Government directives focused on anti‑tamper have sharpened program-level requirements for defense suppliers; commercial sectors are also seeing compliance pressure as state privacy laws and industry standards evolve.
- Technology convergence: Expect tighter integration between runtime application self-protection (RASP), AI-enabled anomaly detection, and traditional code-hardening techniques—security stacks are becoming layered and contextual.
- Talent and delivery: Sophisticated anti-tamper controls require specialized DevSecOps expertise; our models show labor is a key driver of early deployment costs and determines speed-to-value.
- M&A and consolidation signals: Recent asset transfers and product launches point to consolidation in certain subsegments and rapid productization in others—buyers should watch vendor roadmaps for strategic alignment with their own product lifecycles.
Competitive Landscape: Key Players and Strategic Postures
The anti-tamper vendor ecosystem spans pure-play application hardening specialists, rights-management incumbents, hardware-centric providers and newer no-code entrants. Below is a synthesis of positioning and implications for buyers—detailed vendor scorecards and comparative matrices are available in the full brief.
- Digital.ai (Boston): A mature platform player with strong in-app protection across mobile, IoT, web and enterprise workloads. Strategic buyers will find value in Digital.ai’s breadth—especially when they require integrated code obfuscation, white-box cryptography and RASP across heterogeneous environments.
- Guardsquare (Leuven): Deep mobile specialization—known for comprehensive Android and iOS hardening suites. Guardsquare is an attractive partner for organizations prioritizing native mobile code protection and sophisticated obfuscation techniques.
- Verimatrix (Meyreuil): Historically strong in media and conditional-access contexts; recent portfolio shifts (including asset transactions) signal a strategic refocus in its product mix. Buyers should validate roadmap continuity and intellectual property ownership post-transaction.
- Appdome (Boston/Redwood City area): A no-code platform that is gaining momentum across mobile security use cases, evidenced by recent third-party recognitions. Appdome is particularly compelling for organizations seeking rapid time-to-protection with minimal engineering lift.
- Irdeto / Denuvo: A hybrid of game/content protection and broader application shielding; suitable for entertainment and high-value IP contexts where anti-piracy and anti-tamper are tightly coupled.
- Hardware & cryptography specialists (Rambus, Secure‑IC): Provide complementary, tamper-resistant IP for environments where software-only controls are insufficient—defense, critical infrastructure, and secure processing platforms are primary use cases.
- Rights management and application security vendors (Intertrust, OneSpan, PreEmptive, PACE Anti‑Piracy, Waratek, Pradeo, Promon): Offer differentiated capabilities across DRM, runtime protection and specialized obfuscation—buyers should select based on integration needs, regulatory constraints, and target threat models.
Recent market activity underscores shifting competitive dynamics: a high-profile asset transaction involving a mobile protection portfolio was completed in late 2025, and no-code mobile protection platforms posted significant market recognition in early 2026. Meanwhile, IP-focused vendors continue to expand hardware-assisted tamper detection options—signaling increased heterogeneity in solution architectures.
What the PW Consulting Brief Contains (Practical, Executable Resources)
- Vendor scorecards and decision matrix: Side-by-side evaluation criteria keyed to real-world use cases (finance, gaming, automotive/IoT, media, government/healthcare).
- Integration playbooks: Step‑by‑step checklists for embedding anti‑tamper controls in CI/CD pipelines, app stores submission flows and device firmware update processes.
- Threat-to-control mapping: Attack scenarios mapped to specific mitigations (code obfuscation, RASP, white-box crypto, environment checks), with recommended validation tests.
- Total cost of ownership models: Easily parameterized TCO templates that factor licensing, engineering labor, verification testing and incident response overheads.
- Compliance mapping: Concrete control mappings to regulatory frameworks and program protection policies, enabling audit-ready documentation.
- Executive briefings & procurement templates: RFP language and commercial negotiation playbooks to accelerate vendor selection and contracting.
Decision Framework for 2026: Three Strategic Paths
Based on the brief’s findings, PW Consulting recommends that organizations align anti-tamper choices to one of three strategic paths—each with distinct resource, risk and time-to-value profiles:
- Rapid containment (Speed-first): Adopt no-code or managed platform protections to quickly raise the bar against opportunistic tampering. Best for regulated consumer apps and time-sensitive releases.
- Embedded resilience (Engineering-first): Integrate hardware-assisted and build-time obfuscation for long-lived products where IP protection and persistent device security are paramount.
- Program protection (Policy-first): For defense and strategic commercial programs, use a hybrid approach—contractual protections, supplier vetting, and layered technical controls tailored to program-protection guidance.
We provide a compact checklist in the full brief that operational teams can use to classify their application portfolio, estimate incremental effort, and select an adoption path that aligns to enterprise risk tolerance.
What We’re Not Releasing Here (Why You Should Review the Full Brief)
This preview intentionally omits granular regional and vertical revenue splits, vendor market-share tables and specific price-point comparisons—these are available in the full PW Consulting report. The high-resolution tables and model workpapers are essential when you are preparing procurement documentation, negotiating vendor SLAs, or aligning multi-year security roadmaps.
Action Steps for 2026
- Request the full brief for access to detailed regional, deployment-mode and vertical breakouts and for vendor‑level scorecards tailored to your use cases.
- Run a rapid portfolio classification exercise (we provide a one‑page template) to determine which applications require immediate protection vs. those that can be staged.
- Budget for specialized DevSecOps resources; our TCO models demonstrate labor as a gating factor in early adoption cycles.
- Incorporate anti‑tamper requirements into RFPs and supplier evaluations to avoid technical and contractual surprises during implementation.
PW Consulting’s Anti‑Tamper Software Market brief is designed to convert market intelligence into measurable decisions. For 2026, the difference between defensive posture and true program protection will be determined not by vendor logos but by the clarity of your adoption path—and the readiness of your teams to operationalize protection.
For detailed analysis of this topic, please visit the official page: Anti Tamper Software Market
Lacy Lee
Senior Marketing Manager
sales@pmarketresearch.com
00852-95632430
PW Consulting: www.pmarketresearch.com
Tags



PW Consulting
The Best-reviewed Subdivided Market Risk Analysis Firm in the US and East Asia.


