



PW Consulting: Application Security Software Market to Reach $614.7M by 2032, 10.4% CAGR

Strategic Imperatives in the Application Security Software Market: A 2032 Outlook for Enterprise Leaders
As organizations accelerate their digital transformation journeys, the perimeter of corporate defense has shifted decisively from network edges to the application layer itself. The proliferation of cloud-native architectures, microservices, and API-driven ecosystems has expanded the attack surface, making application security no longer a mere compliance checkbox but a core business enabler. For C-suite executives and security architects navigating the complexities of 2026 and beyond, understanding the trajectory of the Application Security Software Market is essential for allocating capital, mitigating risk, and maintaining competitive resilience.
Our latest comprehensive market research offers a rigorous examination of this evolving landscape, synthesizing historical performance data with forward-looking projections to equip decision-makers with the intelligence required for strategic planning. This article serves as an executive overview of the key themes, growth drivers, and competitive dynamics captured in the full report. While we highlight the macro-level trajectories and structural shifts reshaping the industry, the granular segmentation data, detailed vendor benchmarking, and actionable investment frameworks are reserved for the complete study. We invite you to explore the full report to unlock the precise metrics and segmented intelligence necessary for your organization's specific context.
The Macro Trajectory: Sustained Growth in a High-Stakes Environment
The Application Security Software Market has demonstrated remarkable resilience and expansion over the past half-decade, reflecting the non-negotiable nature of software protection in modern enterprise operations. Historical data from 2020 through 2025 reveals a consistent upward trend, with the market growing from approximately 248.5 million USD to 311.0 million USD. This progression underscores a fundamental shift in how organizations prioritize security investments, moving beyond reactive measures toward proactive, integrated application defense strategies.
Looking ahead, the forecast period from 2026 to 2032 indicates that this momentum will not only continue but accelerate. The market is projected to reach 333.15 million USD in 2026, representing a meaningful step up from the previous year, and is expected to climb steadily to 614.7 million USD by 2032. This trajectory reflects a compound annual growth rate of 10.4 percent, signaling sustained demand driven by escalating threat sophistication, regulatory mandates, and the widespread adoption of cloud-native application architectures. For enterprise leaders, this growth rate translates into an expanding ecosystem of solutions, increased vendor competition, and evolving best practices that must be carefully monitored to avoid technological obsolescence and ensure optimal security posture.
The sheer scale of data generation further amplifies the urgency of these investments. As noted by the Security Industry Association in November 2025, the world is expected to generate 181 zettabytes of data in 2025, marking a 23 percent year-over-year increase. This exponential data growth directly correlates with increased application complexity and surface area, reinforcing the need for robust, scalable application security tools that can keep pace with information volume without compromising performance or user experience.
Regulatory Pressures and the New Compliance Imperative
The regulatory landscape has become a primary catalyst for application security adoption, reshaping how organizations approach software development and deployment. European digital sovereignty requirements are intensifying, driven by Regulation (EU) 2025/37, as highlighted by ENISA in June 2025. This shift reflects a broader geopolitical and economic push toward self-reliance in digital infrastructure, compelling organizations operating within or alongside European markets to align their security strategies with localized standards and data governance frameworks.
Equally significant is the introduction of the Cyber Resilience Act, which imposes direct digital product cybersecurity obligations on software suppliers. This legislation moves beyond traditional enterprise procurement requirements, placing responsibility squarely on the shoulders of developers and vendors to ensure that applications meet stringent security benchmarks before reaching the market. For enterprises that develop or procure software, this regulatory evolution necessitates a fundamental rethinking of application security lifecycles, from initial design through continuous runtime protection.
These regulatory dynamics are not isolated to Europe. Global regulatory convergence is creating a complex compliance environment where organizations must navigate overlapping mandates across jurisdictions. The full report delves into how these regulatory forces influence procurement decisions, technology selection criteria, and the long-term cost structure of application security programs, providing a nuanced view that goes beyond surface-level compliance checklists.
Technology Segmentation and the Evolution of AppSec Tooling
The application security software landscape is characterized by a diverse array of tooling categories, each addressing distinct phases of the software development lifecycle and operational environments. The market encompasses static code analysis tools, which examine source code for vulnerabilities before execution; dynamic code analysis tools, which test running applications for runtime weaknesses; and software composition analysis tools, which assess third-party and open-source components for known vulnerabilities and licensing risks. This tripartite structure reflects the comprehensive approach required to secure modern applications, where threats can emerge at any point from code commit to production deployment.
As organizations mature their security programs, the integration of these tooling categories into cohesive platforms is becoming increasingly prevalent. The demand for unified visibility, automated remediation, and continuous monitoring is driving consolidation trends, with vendors expanding their portfolios to offer end-to-end application protection. The report provides a detailed mapping of how these technology categories are evolving, including adoption patterns, integration challenges, and the emerging capabilities that are setting new industry benchmarks. Decision-makers will find value in understanding how these segments interact and which combinations yield the most effective security outcomes for different organizational profiles.
Competitive Dynamics: A Consolidated Landscape with Differentiated Leaders
The application security market is marked by a high degree of concentration, with a small number of dominant players capturing a significant share of overall revenue. Analysis indicates a CR3 of 62.3 percent and a CR5 of 78.1 percent, reflecting an environment where established vendors leverage extensive product portfolios, global sales channels, and deep customer relationships to maintain market leadership. This concentration has implications for procurement strategy, pricing dynamics, and the pace of innovation, as competitive pressure drives both consolidation and differentiation.
Application Security Software Market
Several key companies exemplify the strategic positioning and technological focus that define the current competitive landscape. Palo Alto Networks, headquartered in Santa Clara, California, has centered its application security strategy on the Prisma platform, which includes a dedicated Application Security module. This offering provides cloud-native posture management, runtime protection, and API security, reflecting a holistic approach that aligns with the shift toward cloud-first architectures. Fortinet, based in Sunnyvale, California, emphasizes its FortiWeb and FortiApplication Security Fabric solutions, delivering web application protection, WAF capabilities, and API security across hybrid environments. This breadth of coverage appeals to organizations seeking unified protection across on-premises and cloud deployments.
Imperva, headquartered in San Mateo, California, has built a strong reputation through its Application Security and Data Security portfolio, with a particular focus on Web Application and API Protection (WAAP), WAF, and DDoS mitigation. The company's market recognition is underscored by independent evaluations, including KuppingerCole's 2025 WAAP Report, which named Imperva an overall leader, and the Forrester Wave 2025 for Web Application Firewall Solutions, which recognized Imperva as a security leader. These accolades highlight the company's sustained investment in both technology and market validation.
Cisco Systems, based in San Jose, California, leverages its extensive networking heritage to deliver Cisco Secure Firewall and application security solutions that support zero-trust application delivery and threat protection. This network-integrated approach resonates with organizations seeking to align security controls with underlying infrastructure. Check Point Software Technologies, headquartered in Tel Aviv, Israel, focuses on Harmony SASE and application security solutions, emphasizing API protection and WAF capabilities within a broader secure access service edge framework. F5 Networks, based in Seattle, Washington, concentrates on BIG-IP and Application Security solutions designed for API, web, and application delivery protection in multicloud environments, addressing the complexities of modern traffic management and security enforcement.
Worldwide Application Security Solution Market
The full report provides an in-depth competitive analysis, including vendor profiles, strategic positioning, product capabilities, and market share dynamics. It offers a granular view of how these companies are responding to market demands, innovating their portfolios, and competing for enterprise contracts. This level of detail is essential for organizations evaluating vendor partnerships, assessing technology roadmaps, and making informed procurement decisions.
Enterprise Adoption Patterns and the SME Challenge
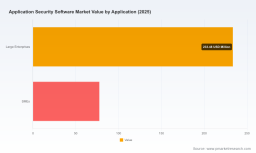
Adoption of application security software varies significantly across organizational sizes, reflecting differences in budget, risk tolerance, technical expertise, and regulatory exposure. Large enterprises represent the dominant segment, driven by expansive application portfolios, stringent compliance requirements, and the resources to implement sophisticated security programs. SMEs, while growing in adoption, face distinct challenges related to cost constraints, talent shortages, and the need for streamlined, easy-to-deploy solutions that deliver immediate value without requiring extensive security operations overhead.
The report examines how these adoption patterns are evolving, highlighting the factors that influence purchasing decisions across different organizational profiles. It explores the role of managed services, cloud-based delivery models, and integrated security platforms in lowering barriers to entry for smaller organizations, while also analyzing how enterprises are scaling their application security programs to match the complexity of their digital ecosystems. Understanding these dynamics is critical for tailoring security strategies to organizational realities and ensuring that investments yield measurable risk reduction.
Operational Considerations: Infrastructure, Costs, and Strategic Alignment
Beyond technology selection, successful application security programs require careful consideration of operational factors, including infrastructure costs, integration complexity, and alignment with broader business objectives. The exponential growth in data generation puts pressure on security infrastructure, requiring solutions that can scale efficiently without incurring disproportionate cost increases. Organizations must balance the need for comprehensive protection with the realities of budget constraints, ensuring that security investments are optimized for both coverage and efficiency.
Strategic alignment is equally important. Application security must be integrated into the fabric of software development, DevOps practices, and cloud operations, rather than treated as a separate, siloed function. This requires cross-functional collaboration, clear governance frameworks, and metrics that tie security outcomes to business risk reduction. The full report provides actionable frameworks for aligning application security investments with organizational priorities, including guidance on capability mapping, vendor evaluation, and program maturation.
What the Full Report Delivers: A Roadmap for Informed Decision-Making
Our comprehensive Application Security Software Market research is designed to serve as a strategic reference for executives, security leaders, and technology procurement professionals. The study delivers a multi-dimensional view of the market, combining historical analysis, forward-looking projections, segmentation insights, and competitive intelligence into a cohesive narrative that supports informed decision-making. Key components include detailed market sizing and growth forecasts, segmentation analysis across regions, technology types, and application profiles, competitive landscape mapping with vendor profiles and strategic positioning, regulatory and industry context analysis, and actionable recommendations for investment and program development.
While this article has provided an executive-level overview of the market's trajectory, the underlying structural drivers, and the competitive players shaping the industry, the full report contains the depth and precision required to translate strategic awareness into operational action. It offers the granular data points, comparative analyses, and nuanced interpretations that enable organizations to benchmark their current posture, identify gaps, and prioritize investments with confidence.
For leaders seeking to navigate the complexities of application security in 2026 and beyond, the full study provides the intelligence foundation necessary to make decisions that are both strategically sound and execution-ready. We encourage you to access the complete report to explore the detailed findings, segmented breakdowns, and vendor-specific insights that will directly inform your organization's security roadmap.
The application security landscape is evolving rapidly, driven by technological innovation, regulatory change, and the relentless creativity of threat actors. Organizations that invest in understanding this landscape and align their security strategies accordingly will be best positioned to protect their digital assets, comply with emerging mandates, and sustain growth in an increasingly interconnected world. Our research is intended to be a trusted partner in that journey, offering clarity, depth, and actionable insight at every step.
For detailed analysis of this topic, please visit the official page: Application Security Software Market
Lacy Lee
Senior Marketing Manager
sales@pmarketresearch.com
00852-95632430
PW Consulting: www.pmarketresearch.com
Tags



PW Consulting
The Best-reviewed Subdivided Market Risk Analysis Firm in the US and East Asia.


