



DNS Security Software Market: Why 8.9% CAGR and Cloud Shift Change Everything

DNS Security Software Market: Strategic Shifts and Commercial Opportunities in a Reshaping Domain Defense Landscape
The DNS Security Software market is entering a period of accelerated structural transformation, driven by converging pressures in cloud migration, regulatory mandates, and increasingly sophisticated DNS-layer attacks. Market estimates place total revenue at approximately $170.0 million in 2025, with historical growth from 2020 through 2025 reflecting a steady acceleration as organizations progressively re-architect their security perimeters around identity and traffic visibility. Forecasts project the market to reach $310.0 million by 2032, representing a compound annual growth rate of 8.9% over the 2026–2032 period. This trajectory signals more than incremental demand growth; it reflects a fundamental reorientation of how organizations treat DNS—not as a passive directory service, but as an active security control point that must be continuously monitored, encrypted, and secured against both volumetric and application-layer threats.
For executives and strategy teams, the commercial implication is clear: DNS security is no longer a niche add-on within broader network protection portfolios. It is becoming a core component of zero-trust architectures, hybrid-cloud resilience programs, and compliance-driven security budgets. Yet the market is also navigating several inflection points that will separate winners from laggards over the next five years. Understanding where momentum is building—and where friction remains—provides a foundation for portfolio decisions, vendor selection, and investment timing.
Market Landscape and Core Challenges
The current market environment is characterized by rising deployment volumes, expanding regulatory expectations, and a persistent mismatch between organizational maturity and the operational complexity of DNS protection. Demand has been sustained by the expansion of cloud-hosted workloads, the proliferation of remote and hybrid work patterns, and an increase in DNS abuse vectors ranging from cache poisoning and tunneling to DDoS amplification. At the same time, buyers are confronted with a fragmented vendor landscape in which capabilities vary widely across threat intelligence integration, posture management, encryption support, and operational simplicity.
Inflection Point 1: DNS as a Security Control, Not Just Infrastructure
Historically, DNS management and DNS security were often treated separately, with networking teams handling resolution reliability and security teams focusing on perimeter and endpoint controls. That division is breaking down. Modern threat campaigns exploit the DNS layer to exfiltrate data, command compromised hosts, and bypass traditional inspection points. As a result, organizations are reassessing DNS security as a first-line control that must be integrated into broader security operations. This shift creates both opportunity and execution risk: organizations that succeed are those that can unify visibility, automate response, and embed DNS protections into existing workflows, while organizations that treat DNS tools as standalone point solutions risk operational silos and coverage gaps.
Inflection Point 2: Regulatory Acceleration and Procurement Mandates
Policy pressure is rapidly reshaping purchasing criteria. In the United States, executive guidance now requires support for encrypted DNS protocols as a procurement requirement for products acting as DNS resolvers for federal agencies, effectively tilting demand toward solutions that natively support encrypted resolution paths and demonstrate compliance readiness. Concurrently, CISA guidance emphasizes enterprise investment in AI-enabled DNS capabilities to address attacks targeting critical infrastructure, pushing buyer expectations toward analytics and automated detection functions. In Japan, national cybersecurity strategy documents are reinforcing the adoption of AI-enabled threat detection within DNS protection programs. These directives do not merely raise awareness; they create procurement momentum, especially among public-sector buyers and regulated industries, where compliance considerations increasingly influence vendor shortlists.
Inflection Point 3: Operational Complexity in Hybrid and Multi-Cloud Environments
As organizations distribute workloads across on-premises environments, multiple cloud providers, and edge deployments, DNS assets become dispersed and harder to inventory, monitor, and secure consistently. The operational burden includes managing authoritative and recursive resolvers, ensuring consistent policy enforcement, and detecting misconfigurations that can expose services to hijacking or denial-of-service conditions. This complexity is a central barrier to adoption for many mid-sized organizations, where staffing constraints limit the ability to operate advanced DNS security tools without agentless, automated, or managed approaches.
Key Drivers Shaping Market Momentum
Technology Innovation: Cloud-Native Resolution, Encrypted Protocols, and AI-Enabled Detection
Technological evolution is one of the strongest catalysts for market expansion. Cloud-native DNS architectures are increasingly favored for their scalability, centralized policy management, and integration with broader security ecosystems. Encrypted DNS protocols are no longer optional enhancements in many procurement contexts; they are becoming baseline expectations for privacy, tamper resistance, and compliance. Equally important, AI-enabled detection and analytics are moving from experimental features to operational requirements, particularly for identifying anomalous query patterns, detecting domain generation algorithms, and reducing response time during active incidents. Vendors that can combine reliable resolution, encrypted transport, and actionable threat intelligence are positioned to capture demand from organizations seeking to consolidate tools and improve security outcomes.
Policy and Regulatory Environment: Mandates as Adoption Accelerators
Regulatory developments are functioning as adoption accelerators rather than abstract compliance checkboxes. Encrypted DNS requirements in federal procurement create downstream pressure on suppliers serving government accounts and the broader supply chain. Sector-specific guidance that calls for AI-enabled DNS protections signals an expectation that critical infrastructure and high-risk industries will invest in more advanced detection and response capabilities. For vendors, this environment rewards clear compliance narratives, documented control mappings, and demonstrable integration with security operations workflows. For buyers, it introduces a practical urgency to evaluate whether existing DNS protections meet evolving expectations for encryption, visibility, and automated detection.
Demand-Side Change: Larger Attack Surfaces and Rising Business Risk
Demand is expanding because the cost of DNS abuse is becoming more visible and more consequential. Phishing, malware command-and-control, data exfiltration, and service disruption are all enabled or amplified by DNS manipulation, and these outcomes carry direct operational, financial, and reputational consequences. Enterprise buyers are increasingly linking DNS security to resilience objectives: ensuring that external-facing services remain reachable, that internal resolution is trustworthy, and that anomalous traffic can be identified before it escalates. This risk-based framing supports budget allocation even in cost-conscious planning cycles, because DNS-layer protections are often positioned as relatively low-friction controls with high preventive value.
Supply-Side and Cost-Structure Dynamics: Integration, Automation, and Service Models
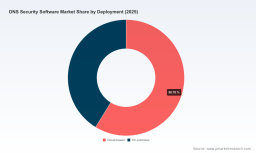
On the supply side, market dynamics are shaped by the push toward integrated platforms, automation, and flexible deployment models. Cloud-based delivery continues to attract interest because it reduces the operational overhead associated with maintaining and updating on-premises resolver infrastructure, while also simplifying expansion across distributed locations. At the same time, on-premises deployments remain relevant in scenarios where data residency, latency sensitivity, or existing network architectures favor local control. The broader cost-structure trend is toward solutions that lower ongoing staffing demands through agentless visibility, automated remediation, and managed services options. This evolution is particularly important for smaller and mid-sized organizations that need enterprise-grade protections without proportional increases in specialized personnel.
Domain Name System Tools Market
Competitive Landscape and Leading Strategies
The competitive environment is defined by a mix of incumbent infrastructure vendors, cloud and networking specialists, and providers with strong DNS heritage. Market concentration remains moderate, with the top three firms collectively representing roughly 25% of revenue and the top five reaching approximately 38%. This level of concentration suggests a market that is still fragmented enough for differentiation to matter, while also indicating that scale, ecosystem reach, and integrated portfolios provide meaningful advantages.
Differentiation Through Integration, Intelligence, and Resilience
Leading players are pursuing distinct strategic positions. Cisco Systems emphasizes cloud-delivered DNS-layer protection integrated with threat intelligence, aiming to block malware, phishing, and related threats before connections are established. Infoblox focuses on protective DNS and threat defense designed to safeguard DNS infrastructure against hijacking, cache poisoning, and DDoS attacks, appealing to organizations that prioritize DNS integrity as a core operational requirement. Cloudflare builds on its resolver and DNS firewall offerings by embedding DDoS mitigation, DNSSEC, and malware blocking for both enterprise and consumer contexts, leveraging its broader network presence to position DNS protection as part of a wider edge security model. Akamai Technologies emphasizes DDoS-resilient DNS delivery and posture management for hybrid cloud security, targeting organizations that need robust availability and visibility across complex environments. F5 Networks positions its DNS offerings around advanced security, load balancing, and protection against DNS attacks in hybrid settings, which resonates with enterprises seeking to align traffic management and security controls. Verisign and Neustar draw on established DNS infrastructure expertise, offering threat intelligence, DDoS protection, and managed DNS services that support enterprises and critical infrastructure scenarios.
PW Consulting Information & Electronics Research Center
The differentiating factors that matter most in this landscape are not limited to feature checklists. Buyers increasingly evaluate the breadth of threat intelligence integration, the quality of visibility across hybrid environments, the practicality of automated response, and the ability to meet procurement requirements for encrypted DNS. Providers that can connect DNS security to broader security operations, cloud governance, and compliance workflows are better positioned to win multi-year commitments.
Recent Developments and Evolving Market Structure
Recent product and partnership activity illustrates how vendors are closing capability gaps and expanding distribution. In June 2025, Akamai introduced DNS Posture Management, an agentless solution designed to provide unified multicloud visibility over DNS assets for real-time monitoring and remediation. This type of offering reflects a broader trend toward visibility and configuration governance as prerequisites for reliable DNS protection, especially where environments span multiple cloud providers. In September 2024, IGIT partnered with NS1 and Cisco to deliver agile DNS security application deployments targeting the EMEA region, demonstrating how channel and technology partnerships can accelerate regional reach and deployment flexibility.
These moves point to a market in which differentiation is increasingly tied to visibility, automation, and ecosystem enablement rather than standalone DNS features alone. The competitive trend is not simply toward consolidation; it is toward layered value propositions in which DNS security becomes embedded in multicloud operations, edge security, and compliance programs. New entrants and specialist providers can still compete by addressing niche requirements—such as specific compliance frames, high-scale DDoS resilience, or verticalized threat detection—while larger vendors compete on breadth, integration, and operational scale.
Forward Outlook: Three Trends Shaping the Next 3–5 Years
Trend 1: Encryption and AI-Enabled Detection Become Baseline Expectations
Over the next several years, the combination of encrypted DNS and AI-enabled detection is likely to shift from differentiated capability to baseline expectation, especially in regulated and publicly exposed environments. Encrypted resolution paths will increasingly be required not only for privacy but also for procurement alignment and tamper resistance. AI-driven analytics will be expected to support faster triage, anomaly detection, and policy refinement. The commercial opportunity for vendors lies in delivering these capabilities in ways that are operationally practical: integrated into existing security tools, explainable to analysts, and measurable in terms of detection and response improvements. The risk for buyers is assuming that advanced features automatically translate into reduced operational overhead; without integration and governance, AI-enabled tools can add complexity rather than remove it.
Trend 2: DNS Posture Management and Multicloud Visibility Gain Strategic Importance
As multicloud adoption deepens, DNS posture management and unified visibility will become more central to security programs. Organizations will need to inventory DNS assets across environments, detect misconfigurations, and enforce consistent policies without relying entirely on manual audits or highly specialized staff. Agentless and automated approaches are likely to gain traction because they reduce the friction of expanding coverage across new workloads and locations. The commercial opportunity here extends beyond detection to remediation and governance: solutions that help teams maintain DNS hygiene, validate configuration changes, and respond quickly to deviations are well positioned to become part of ongoing operational budgets rather than one-time project spend.
Trend 3: Verticalized Demand and Compliance-Linked Procurement Intensify
Demand is likely to become more verticalized as industry-specific risk profiles and regulatory expectations diverge. BFSI, healthcare, government, and critical-infrastructure-adjacent sectors are already among the more pronounced areas of adoption interest, and further guidance or procurement requirements could intensify focus on DNS protections in these domains. This trend favors providers that can articulate clear control mappings, demonstrate sector-relevant threat coverage, and provide deployment flexibility for environments with distinct privacy, residency, or availability constraints. The uncertainty lies in the pace and consistency of regulatory evolution: while some jurisdictions are advancing clear directives, others may Lag, creating uneven demand patterns across regions and industries.
Strategic Recommendations for Decision Makers
For vendor and product leaders, the strategic imperative is to move beyond DNS security as a feature narrative and toward integrated outcomes. Solutions that combine reliable resolution, encrypted protocols, threat intelligence, and automated posture management will be better positioned to compete in procurement environments where buyers seek consolidation and operational simplicity. Differentiation should be expressed in terms of deployment flexibility across cloud and on-premises contexts, the practicality of integration with security operations, and the clarity of compliance support. Partnerships, particularly those that expand regional reach or enable faster deployment in complex environments, can be decisive in shortening sales cycles and broadening addressable segments.
For investors, the market’s growth trajectory and moderate concentration suggest that value creation will come from both scale advantages and targeted differentiation. Due diligence should examine not only revenue momentum but also the defensibility of threat intelligence pipelines, the operational burden of the deployed architecture, and the extent to which offerings are aligned with procurement requirements for encrypted DNS and AI-enabled detection. Capital allocation decisions should weigh the potential for platform consolidation against the persistence of specialist niches, particularly in DDoS resilience, critical infrastructure support, and verticalized compliance contexts.
For enterprise buyers and procurement teams, the priority is to treat DNS security as a continuum rather than a single purchase decision. Evaluations should consider encrypted protocol support, visibility across hybrid and multicloud assets, integration with existing security tooling, and the operational model required to keep protections current. Organizations should also assess whether they have sufficient internal capability to manage posture, respond to anomalies, and maintain configuration hygiene, or whether managed services, automation, or agentless approaches are needed to close gaps. Because requirements are evolving quickly, access to detailed segmentation insights, vendor benchmarking, and deployment-pattern data can materially improve buying and planning decisions.
Application Security Software Market
Detailed market segmentation, vendor-level benchmarking, and region- and industry-specific deployment dynamics remain essential for firms that need to act with precision rather than rely on aggregated trends alone. For leaders seeking deeper coverage of demand patterns, competitive positioning, and tailored recommendations across sectors and deployment contexts, the full PW Consulting research report provides the granular data and scenario analysis needed to translate market momentum into concrete strategy.
For detailed analysis of this topic, please visit the official page: DNS Security Software Market
Lacy Lee
Senior Marketing Manager
sales@pmarketresearch.com
00852-95632430
PW Consulting: www.pmarketresearch.com
Tags



PW Consulting
The Best-reviewed Subdivided Market Risk Analysis Firm in the US and East Asia.


